Cryptographic Discovery: How to Build a PQC Cryptographic Inventory
Cryptographic discovery is the process of identifying where cryptography is used across an organisation's systems, applications, infrastructure and services. For post-quantum cryptography (PQC) readiness, that means looking beyond certificates to algorithms, keys, protocols, cryptographic libraries, authentication mechanisms and dependencies.
No single discovery method can provide complete visibility. Network scanning, source-code analysis, container scanning, certificate lifecycle management and existing asset data each reveal different parts of the cryptographic landscape.
The objective is to combine these sources into a maintainable cryptographic inventory that can support risk analysis, crypto-agility and PQC migration planning.
What is the difference between a certificate inventory and a cryptographic inventory?
A certificate inventory tracks certificates and their associated properties and lifecycle. A cryptographic inventory is broader: it identifies the cryptographic assets and dependencies used across an organisation's technology environment.
Certificates are an important part of the picture, but they're only one layer.
A broader cryptographic inventory can include:
- algorithms
- cryptographic libraries
- protocols
- keys
- certificates
- cryptographic use within applications and code
- authentication mechanisms
- dependencies between cryptographic assets and systems
This distinction becomes particularly important when preparing for post-quantum cryptography.
A certificate inventory can provide visibility into certificates and their lifecycle. But it won't necessarily reveal a cryptographic library embedded inside an application, an algorithm hard-coded into firmware or a dependency on cryptography controlled by a third-party service.
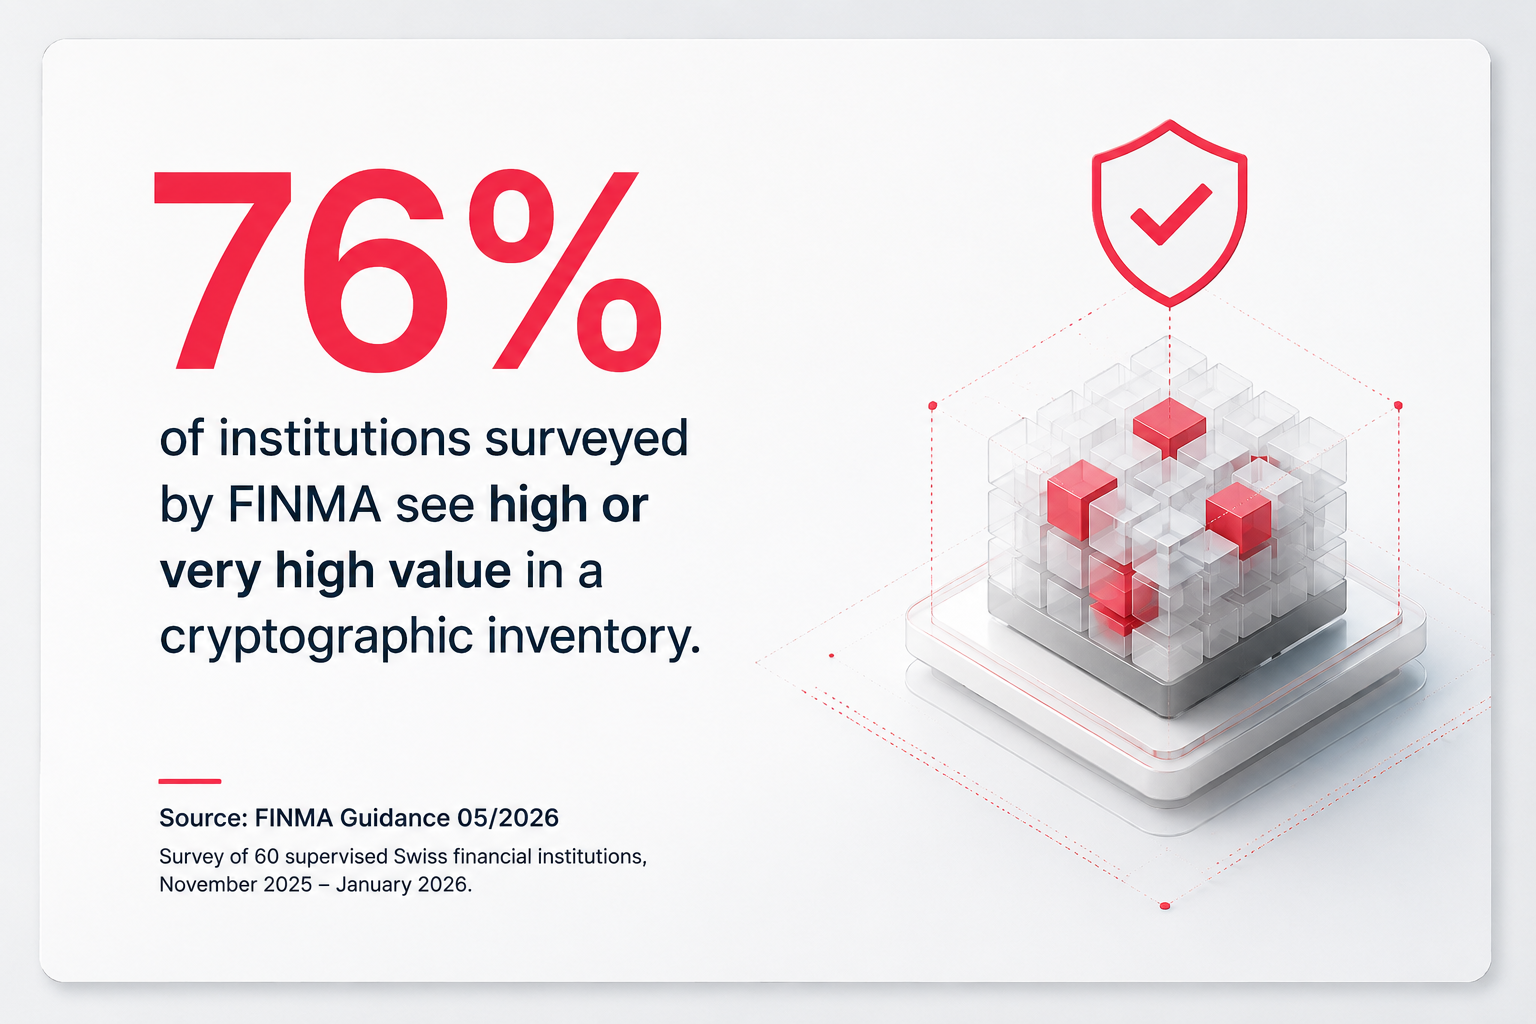
FINMA's own survey reinforces the importance of looking beyond individual cryptographic assets.
76% of institutions surveyed by FINMA see high or very high value in a cryptographic inventory.
Source: FINMA Guidance 05/2026. Survey of 60 supervised institutions conducted between November 2025 and January 2026.
Why can't one tool discover all cryptographic assets?
Cryptography exists at multiple layers of enterprise infrastructure.
Each source answers a different question. The challenge is correlating those discoveries into one usable cryptographic inventory.
What cryptographic discovery methods should organisations use?
A practical discovery methodology combines passive and active network scanning, container-image scanning, static source-code analysis and integration with CMDB and certificate lifecycle management data.
What are the common blind spots in cryptographic discovery?
Even a multi-source discovery approach needs to account for areas that are difficult to see.
A discovery programme should explicitly account for environments that conventional enterprise scanning may not fully cover.
Cloud environments.
Cryptographic assets and dependencies may sit within services that an organisation does not directly operate.
OT environments.
Operational technology can introduce different architectures, ownership models and replacement cycles.
Embedded systems and firmware.
Cryptographic components may be deeply integrated into devices and difficult to identify through conventional enterprise scanning.
Legacy systems.
Older environments can contain cryptographic dependencies that are poorly documented or difficult to change.
Third-party services.
An organisation may depend on cryptography operated outside its own infrastructure.
Application dependencies.
Cryptographic APIs, libraries and hard-coded secrets may sit inside software rather than appearing as obvious network or certificate assets.
These are specifically identified as areas to consider within the campaign's discovery methodology.
The objective therefore isn't simply to produce a longer asset list.
It is to understand:
- Where does cryptography exist?
- What depends on it?
- Who owns it?
- And how difficult will it be to change?
How can a CBOM turn cryptographic discovery into a living inventory?
A Cryptography Bill of Materials (CBOM) is a machine-readable representation of cryptographic assets and their relationships. It can help organisations turn discovery results into structured inventory data that can be queried, updated and integrated into development and operational processes.
Discovery is only the beginning.
A one-off spreadsheet may provide a snapshot, but it won't support a multi-year migration programme if it immediately starts falling out of date.
Applications change.
Infrastructure changes.
Containers are rebuilt.
Libraries are updated.
Certificates are issued and renewed.
New services and dependencies appear.
For a multi-year PQC programme, the cryptographic inventory should be treated as a living dataset rather than a one-time spreadsheet.
One approach is a machine-readable Cryptography Bill of Materials (CBOM).
Using a format such as CycloneDX can make cryptographic inventory information queryable and allow inventory generation to be integrated into development and operational processes.
The campaign methodology specifically identifies a machine-readable CBOM in CycloneDX format and keeping it current through CI/CD as the next step beyond one-off discovery.
That moves the organisation from asking: “What cryptography do we think we have?”
to: “What cryptography is actually deployed, where is it used and what depends on it?”
How does certificate lifecycle management fit into cryptographic discovery?
Cryptographic discovery and certificate lifecycle management solve different but complementary problems. Discovery identifies cryptographic assets and dependencies. Certificate lifecycle management provides operational control over certificates once they are known.
Certificate lifecycle management remains an important part of this broader architecture.
Once certificates have been identified, their issuance, renewal, replacement and policy enforcement can increasingly be automated.
That operational capability matters for crypto-agility.
But certificate lifecycle management and cryptographic discovery solve different parts of the problem.
A cryptographic inventory needs broader visibility across algorithms, libraries, protocols, keys and cryptographic use within applications and systems.
ID Security's CEMA Certificate Lifecycle Manager provides the operational capability to manage and automate certificates across heterogeneous PKI environments.
The campaign therefore draws a clear distinction between cryptographic discovery and inventory and certificate lifecycle management and operational crypto-agility.
Why is cryptographic discovery the first step in PQC migration?
It is to establish enough visibility to make the next decisions possible.
- What cryptography is actually deployed?
- Where are the dependencies?
- Which assets will be difficult to change?
- Where are external providers involved?
- Where are the blind spots?
- Which parts of the environment require deeper investigation?
Only once those questions can be answered does an organisation have the evidence needed to move from assumptions about its cryptographic estate to a structured migration programme.
You can't migrate what you can't see.
And you can't build a reliable cryptographic inventory from a single source.
That is why discovery comes first.
-
Frequently asked questions about cryptographic discovery
What is cryptographic discovery?
Cryptographic discovery is the process of identifying where cryptographic assets and technologies are used across systems, applications, infrastructure and services.
What is a cryptographic inventory?
A cryptographic inventory is a structured record of cryptographic assets and relevant dependencies, which can include algorithms, certificates, keys, protocols, libraries and their use within systems and applications.
Is a certificate inventory the same as a cryptographic inventory?
No. A certificate inventory focuses on certificates, while a cryptographic inventory covers a broader range of cryptographic assets and dependencies.
Why is cryptographic discovery important for PQC?
Organisations need to know where quantum-vulnerable cryptography is used before they can assess risk, establish migration priorities and plan replacement.
Can one tool discover all cryptography?
Different discovery methods provide visibility into different technology layers, so a multi-source approach is generally needed to build a broader inventory.
What is a CBOM?
A Cryptography Bill of Materials is a structured, machine-readable representation of cryptographic assets and their relationships. CycloneDX supports representation of algorithms, certificates, protocols and related cryptographic material.
How does certificate lifecycle management support PQC readiness?
Certificate lifecycle management provides visibility and operational control over certificates, while broader cryptographic discovery identifies cryptographic assets and dependencies beyond certificates.